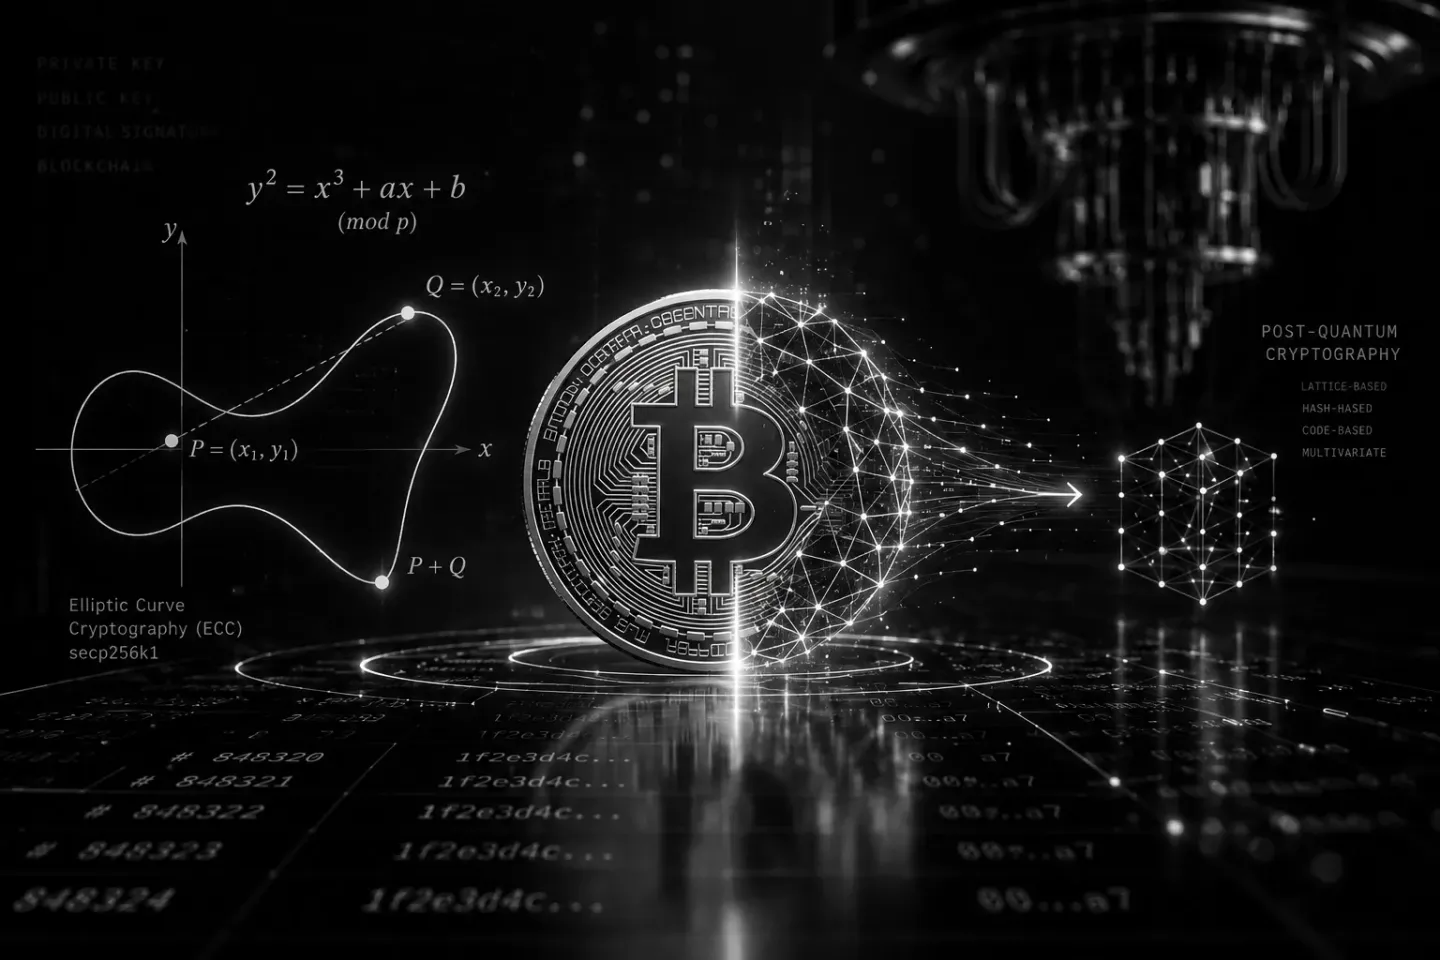

The quantum computing threat to Bitcoin's elliptic curve cryptography (ECC) is established, and the timeline for cryptographically relevant quantum computers (CRQCs) continues to point at the early 2030s. The migration to post-quantum cryptography is underway; output types and signature schemes are under active comparison, and rescue protocols are advancing alongside them. What happens to coins that cannot migrate remains contested.
Each of these is a component of the transition. None of them says how the components resolve together. Outcomes for holders depend on whether the coordination timeline can advance faster than the threat timeline is compressing. That gap is where Bitcoin's quantum computing risk actually sits.
Two of the possible answers on consensus are already well documented: some vulnerable coins will remain unmigrated whatever else happens, and consensus could fracture into a contested fork. The three scenarios below depend on timing rather than on what the network decides.
In the first, the migration finishes with margin to spare. In the second, the market reprices quantum risk long before any capable machine exists. In the third, capability arrives without being announced, and the migration proceeds against a threat estimate that is wrong. Each asks something different of holders, and each has a signal that it is the pressure now in the lead.